DHCP Conflicts in a Growing Office: Find and Fix the Source
In modern business environments, dynamic host configuration protocol (DHCP) misconfiguration or unmanaged scale often leads to disruptive network conflicts—manifesting as duplicate IP assignments, unpredictable connectivity, and security exposures. Singapore’s rapid office expansion and complex hybrid environments make it essential to methodically uncover and eliminate the source of these DHCP problems. This guide provides actionable, in-depth procedures tailored for enterprise and mid-sized IT teams, incorporating granular analysis across Microsoft Windows Server DHCP, Fortinet FortiGate, and Cisco Catalyst environments.
Map DHCP Servers in Your Singapore Office
The foundational step in troubleshooting DHCP overlap or conflicts is developing a precise inventory of all active DHCP servers on-site—including intentional and inadvertent sources. In growing offices, rogue servers often appear through legacy devices, test hardware, or misconfigured coworker laptops.
Methods to Identify DHCP Servers:
- Network Scans: Use protocols such as DHCPDISCOVER and Wireshark to passively scan for servers replying to unknown requests. Multiple responses suggest overlapping scopes or unauthorized DHCP servers.
- Switch ARP Tables: Check the MAC and IP address mappings on your core switch (e.g., Cisco Catalyst). Identify new or unknown devices emitting DHCP traffic.
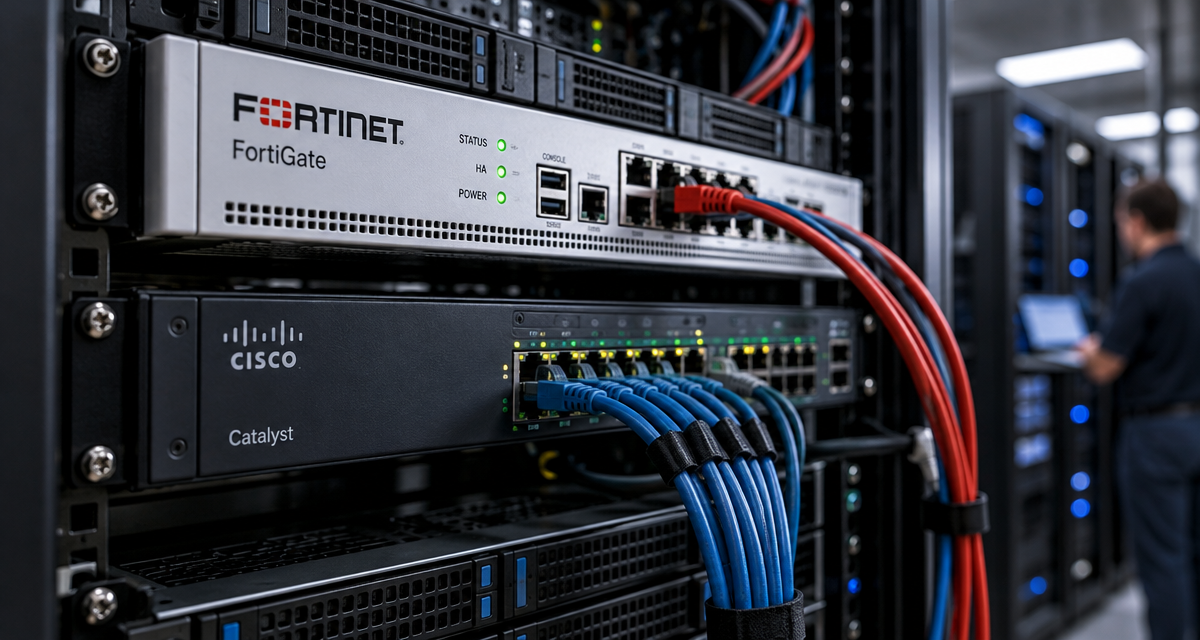
- Server Inventory Review: Examine AD-joined Windows Server DHCP roles, FortiGate interfaces set to DHCP mode, and any embedded appliance DHCP modules.
Technical Friction:
Mapping is rarely straightforward. Older devices might not respect DHCP relay boundaries, and features like Windows’ Automatic Private IP Addressing (APIPA) can mask unauthorized servers. IT teams should enforce port security on switches, disable unused switch ports, and maintain thorough documentation of all networked appliances.
Architectural Benefits:
- Clear DHCP server mapping enables rapid isolation of misconfigurations or rogue servers.
- Prevents cascading issues by reducing the attack surface area for man-in-the-middle or denial-of-service attacks.
- Simplifies post-migration troubleshooting, especially after acquisitions or office expansions.
Check ISP Routers and Added Network Equipment
Many Singapore ISPs provision consumer-grade routers for small offices, which often ship with embedded DHCP services enabled by default. In a growing business, these units may accidentally be left in parallel with enterprise gear—introducing intermittent DHCP offers and duplicate leases.
Areas to Inspect:
- ISP-supplied Gateways: Review configuration interfaces on main and backup routers. Explicitly disable DHCP serving if the function is delegated to a dedicated server or UTM (e.g., FortiGate).
- Third-Party Extenders or Wi-Fi Mesh: Products used for wireless coverage may have their own DHCP functions set to default “on”—commonly missed during deployments.
- Infrastructure Refresh: When replacing or upgrading switches (ex: migration to higher-tier Cisco Catalyst), review internal DHCP relay/serving status, as these settings are sometimes copied over unintentionally during template-based provisioning.
Compatibility & Trade-Offs:
- Disabling DHCP on ISP routers might eliminate their ability to serve as backup fallback when primary DHCP fails. Assess your risk tolerance for single-point-of-failure against the chaos caused by overlapping pools.
- Network appliances from different vendors rarely log or notify DHCP role conflicts between themselves—requiring manual review or automated script auditing.
Integrating network equipment into asset management platforms reduces the risk of configuration drift and allows IT to spot overlapping DHCP roles before they translate into major incidents.
Separate Dynamic Pools From Fixed Addresses
Effective DHCP implementation hinges on a rigorously structured IP address plan. Mixing static and dynamic assignments within the same subnet is a primary cause of recurring network conflicts, especially as device count grows or remote workers return to the office.
Best Practices for Segregation:
- Use IPAM tools or spreadsheets: Explicitly document which IP subranges are reserved for dynamic pools, static addresses (servers, printers, VoIP endpoints), and management infrastructure.
- Enforce via Scopes: In Windows Server DHCP, define explicit exclusions to shield static allocations from being assigned dynamically. On FortiGate, configure non-overlapping address pools per interface.
- Monitor for Collisions: Regularly scan for devices with DHCP-assigned addresses in static ranges—such instances are signals of misalignment or undocumented hardware.
Hidden Trade-Off:
Allocating too narrow a dynamic range can exhaust the pool during peak periods (e.g., onboarding events, hot-desk users, large meetings), causing DHCP declines and failures. Conversely, excessive static assignment kills address utilization efficiency and complicates audits, especially in networks with BYOD and IoT elements.
Separation discipline pays off in operational stability, rapid troubleshooting, and future readiness for IPv6 coexistence or zero-trust segmentation.
Configure Reservations for Business Devices
For critical infrastructure (servers, management laptops, printers, AV hardware), IP reservations are essential. Instead of static IPs directly configured on devices—inviting human error—DHCP reservations ensure consistent IP mapping tied to MAC addresses, centrally visible and modifiable.
Reservation Workflows by Platform:
- Windows Server DHCP: Use the MMC snap-in or PowerShell to map specific MAC addresses to IP reservations in the right scope. Enable reservation options for DNS, routing, or custom options as needed.
- FortiGate: Assign IP addresses or reservations within each interface’s DHCP server settings. Integrate with policies to enforce access controls for critical endpoints.
- Cisco Catalyst: Typically acts as a DHCP relay, but can serve DHCP and reservations for smaller offices. Reservations are entered in the running-config in ‘ip dhcp pool’ mode.
Limitations & Real-World Pitfalls:
- MAC address changes (e.g., after hardware replacement or VM migration) will break reservations unless updated in the DHCP server.
- Some IoT/embedded devices randomize MAC addresses for privacy, complicating reliable reservation assignment.
- Excessive reservations reduce the flexibility of your address pool if the size was not provisioned with growth in mind.
Key Benefits:
- Reservations ensure stable connectivity for monitored devices, reducing troubleshooting friction.
- Easier compliance with network access policies and operational logging/auditing.
- Simpler device replacement and onboarding—change the MAC in the DHCP config, not the device itself.
Set DHCP Relay Across VLANs
Growing offices routinely segment their network with VLANs for security, performance, or compliance. In multi-VLAN environments, centralized DHCP requires relaying requests from all segments to the correct server. If a relay (IP Helper on Cisco, relay agent in FortiGate) is misconfigured or missing, devices on isolated VLANs won’t acquire addresses—while misdirected relays can expose scopes to unauthorized subnets.
Key Implementation Steps:
- Enable DHCP relay (IP helper address) on the gateway interface for each VLAN pointing to the correct DHCP server’s IP.
- Support for multiple relays: FortiGate and modern Cisco Catalyst platforms allow specification of multiple DHCP servers, supporting high availability and failover.
- Monitor logs on your DHCP server for relay IPs and subnet origin—unexpected sources should trigger review for misrouted or malicious relay attempts.
Hidden Complexity:
Enterprise networks with VPN tunnels, guest Wi-Fi islands or cloud-integrated subnets may need careful firewall rules to allow only relay DHCP traffic—not rogue DHCP offers leaking between segments. Legacy switches (early Cisco Catalyst or unmanaged units) may lack proper relay support, requiring hardware or firmware upgrade.
Future-Proofing Consideration:
- DHCP relay configuration should be codified in network automation scripts or infrastructure-as-code templates to avoid drift during scaling or migration.
- With IPv6 adoption, teams must manage DHCPv6 relay agents in parallel.
Locate Unauthorised DHCP Responses
Unauthorized DHCP responders (so-called “rogue DHCP servers”) threaten network stability and security—often resulting from forgotten test VMs, shadow IT, or malware. Finding and eliminating these is non-negotiable for office network hygiene.
Detection Techniques:
- Run DHCP Snooping on managed switches (e.g., Cisco Catalyst): This feature only allows offers from trusted ports (uplinks to legitimate DHCP servers), dropping others and logging events.
- Use packet capture tools (Wireshark, tcpdump) on a client VLAN to spot multiple DHCPOFFER packets for the same request. Note source MAC/IP for investigation.
- Routinely audit device inventory with network access control (NAC) solutions, flagging unauthorized devices running DHCP services.
Operational Limitations:
- DHCP snooping can disrupt operations if configured too aggressively, blocking legitimate server responses during failover events.
- Consumer IoT or “plug-and-play” printers sometimes run their own minimal DHCP servers by default—requiring careful vetting before connecting to production VLANs.
Mitigation is technical and procedural: shut down suspicious switch ports, tighten procurement and onboarding policy, and maintain rapid-response runbooks for neutralizing detected rogues.
Resolve Duplicate Addresses and Pool Exhaustion
Duplicate IP assignment and address pool exhaustion lead to outages and major productivity loss. Both issues occur when DHCP pools are too small, scopes are overlapping, lease times are misconfigured, or rogue servers are active.
Typical Symptoms:
- Devices intermittently kicking each other off the network or being unable to connect.
- Consistent user complaints for “IP address conflict” popups on Windows endpoints.
- Event logs in Windows Server DHCP or FortiGate’s dashboard showing exhausted address pools or frequent NAKs (negative acknowledgements).
Technical Solutions:
- Adjust and expand DHCP scope—balance against subnet mask to avoid overlap with static and reserved addresses.
- Shorten lease time during high-churn events (large meetings, conference events), then revert to standard duration.
- Review MAC-to-IP mapping logs for recurring conflicts; investigate if devices are set with static IPs inside dynamic pools.
- Rogue server scan: Confirm only a single, authoritative DHCP server is responding on each VLAN.
Exhaustion signals a need for subnet review or breaking up address domains—especially in legacy /24 setups that no longer fit a growing office’s real device count.
Test Renewals and Record Scope Ownership
Merely configuring DHCP isn’t enough—ongoing operational stability depends on periodic renewal testing and clear documentation of scope “ownership.” Failing to manage renewal can leave printers or conference room controllers offline for days.
Testing Renewal Scenarios:
- Force device DHCP renewal via ‘ipconfig /renew’ on Windows, `dhclient -r` on Linux, or by toggling network adapters.
- Simulate reboots, network transitions (Wi-Fi to ethernet), and hot-desk workflows at volume to test robustness.
- Monitor for failed renewals in DHCP server logs—often a sign of rogue servers, missing scope definitions, or breakdown in relay infrastructure.
Recording Scope Ownership:
- Document which stakeholder or IT team “owns” each DHCP pool or scope—especially after mergers, office expansions, or multi-country configurations.
- Use comments (where supported) inside DHCP server configs to annotate the function, owner, and approved range per scope.
- Align scope reviews in regular change management cycles, especially during planned scale-ups or network re-segmentations.
Proactive control over DHCP renewals and scope responsibility minimizes firefighting and keeps office technology teams focused on strategic initiatives—not unplanned incident response.
Comprehensive Enterprise DHCP Platform Comparison Table
| Feature/Capability | Microsoft Windows Server DHCP | Fortinet FortiGate | Cisco Catalyst Switch | Target Business Size | Typical Use Case |
|---|---|---|---|---|---|
| Centralized DHCP Management | Full GUI & PowerShell, AD integration | Integrated in UTM interface, CLI & GUI | CLI-based, limited GUI on new models | Mid to Large Enterprise | Central DHCP for Windows-centric offices |
| DHCP Relay Support | Possible, but relies on Layer-3 devices | Native relay agent per interface | IP Helper address for relay | Varies by Layer-3 deployment | Multi-VLAN offices, campus setups |
| DHCP Reservations | Easy reservation via MAC, advanced options settable | Reservation per MAC, bound to policy rules | Basic reservation via config | All sizes; depends on feature use | Critical fixed-IP infrastructure (printers, servers) |
| DHCP Snooping/Detection | Not native, audit via logs/packets | Monitor logs, no native DHCP snooping | Strong DHCP snooping on managed switches | Medium to Large | Detection of rogue DHCP servers |
| Licensing/Costs | Included in Windows Server (from USD $972 per server, CALs required) | Firmware feature; licensed as part of UTM (starts ~$700 per year/device) | Included with switch OS, not separately licensed | All sizes; depends on deployment | Cost-effective for existing infra, high-end for new builds |
| Automation & Scripting | PowerShell, Group Policy, AD-linked | CLI scripts, FortiManager integration | CLI-based automation, some REST API on new units | Enterprise with IT automation | Dynamic, policy-driven environments |
| Integrated Security | Works with NPS, AD, basic security scope options | UTM features: anti-malware, IPS, access policy tie-in | Switchport security, DHCP snooping, radius integration | Secured, regulated industries | Environments needing DHCP tied to device trust |
Summary and Practical Recommendations
As Singapore offices expand, unmanaged DHCP can quickly spiral into recurring outages, security gaps, and user frustration. A structured approach—mapping every DHCP-enabling device, cleaning up overlapping roles on routers and Wi-Fi, meticulously separating address ranges, and enforcing reservations where needed—yields stability at scale. Choose your platform mix with eyes open to costs, operational overhead, scripting potential, and future networking needs.
Top-tier switches, firewalls, and Windows DHCP each bring advantages and constraints—select the combination that fits your business’s size, regulatory environment, and automation maturity. Routine audits, deliberate documentation, and runbooks for incident response transform reactive firefighting into proactive network governance.