Split DNS for Hybrid Teams: Keep Office Services Reachable
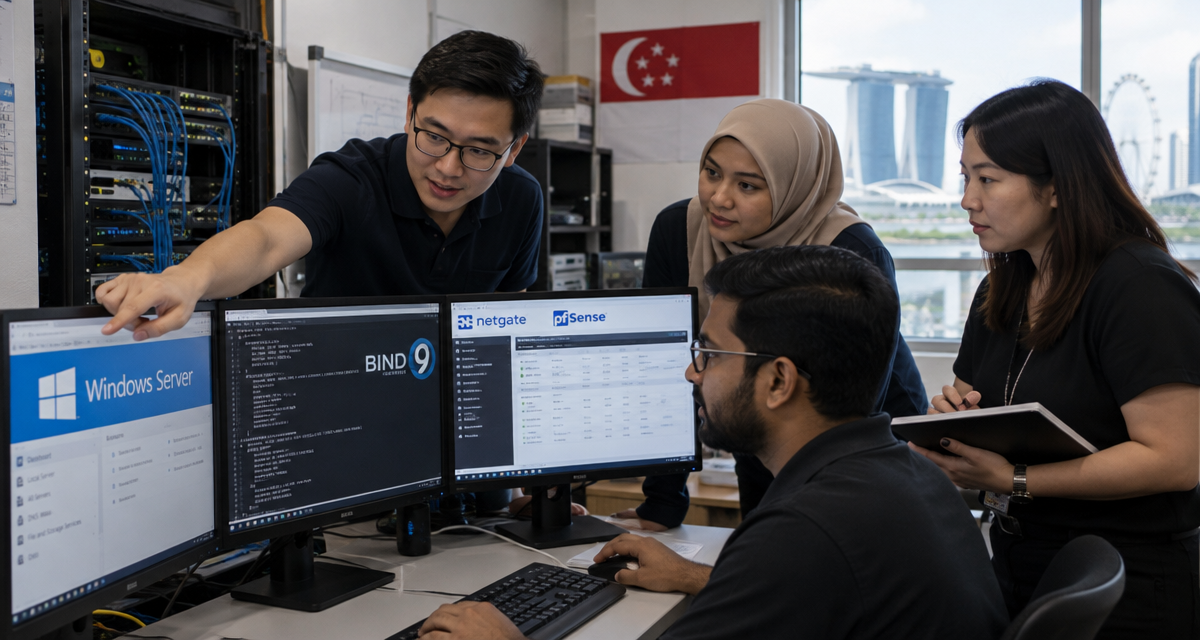
Hybrid work environments—especially in global business hubs like Singapore—demand consistent, secure, and user-transparent access to internal company resources from anywhere. Successful implementation of a split DNS business network strategy ensures that both on-premises personnel and remote workers can reliably connect to internal services with the same familiar service names. Achieving this consistency depends on precisely mapping internal resources, defining dual DNS views, configuring resolvers and VPN integrations, and proactively diagnosing record inconsistencies. This guide dissects the process using Microsoft Windows Server DNS, BIND, and Netgate pfSense, with an analytical focus on real-world implementation friction, trade-offs, and operational resilience.
Map Internal Services Used by Singapore Hybrid Teams
Before configuring any split DNS architecture, IT leaders must catalogue which internal applications and network services their Singapore-based hybrid teams require. The inventory should distinguish services strictly for in-office use, globally accessible cloud workloads, and critical business systems that remote employees also need (finance apps, collaboration tools, version control, VoIP/SIP endpoints, HR platforms).
- Application Discovery: Conduct an audit via traffic analysis or endpoint surveys to locate all relied-upon internal FQDNs (e.g., jira.corp.sg, voip01.office.local).
- Segmentation: Label services as either office-only, remote-access, or public—informs which records must exist split across internal (private) and public zones.
- Dependency Mapping: Document not just primary services but all backend dependencies (databases, authentication endpoints, licensing servers) that influence user access or application stability.
A common operational risk is over-including services in the VPN-required set, which can cause unnecessary bandwidth and privacy burden for users accessing SaaS or non-sensitive resources. Conversely, missing a backend API needed by both local and remote teams can result in lost productivity and protracted troubleshooting. Platform support also varies: Windows Server DNS natively associates service records with Active Directory zones, whereas BIND requires explicit configuration for each view. Netgate pfSense can auto-discover DHCP-registered hosts but may miss statically configured infrastructure unless manually entered.
Define Internal and Public DNS Answers
With resources mapped, businesses must maintain separate DNS answer sets for internal and external clients—even for the same domain names. Typically, this means:
- Internal DNS: Returns private IPs (10.x.x.x, 192.168.x.x) for corporate services when requests come from within the VPN or local office.
- Public DNS: Returns public IPs or proxies, or deliberately withholds records for the same hostnames when the request is from the open internet.
For example, intranet.sgcorp.com should resolve to 10.15.6.11 on the office LAN or via VPN, but be NXDOMAIN (non-existent) or point to a sandbox zone externally. This is crucial for services not meant to be internet-facing. DNS platforms differ in their approach:
- Microsoft Windows Server DNS: Leverages conditional forwarders, zone scopes (with DNS policies), and AD-integrated zones for granular control. GPO enforcement is straightforward for Windows endpoints, but cross-platform and BYOD support can be complex.
- BIND: Uses views to present different zone files based on client source IP/class or ACL. Scalability is excellent, but each additional view increases configuration complexity and risk of misalignment.
- Netgate pfSense: The DNS Resolver (Unbound) can provide split answers, but is best used as a forwarder or caching layer for backend AD/BIND infrastructure. Direct authoritative split DNS is less common but possible for small or branch deployments.
Hidden trade-offs emerge here: Active Directory dependency with Windows Server increases management burden in mixed OS environments, while BIND offers broadest compatibility at the cost of more manual configuration and risk of human error. PfSense’s integration is seamless for simple deployments but may lack advanced role-based delegation or dynamic record features needed in larger enterprises.
Configure Resolvers and Forwarding
Proper DNS resolver and forwarder configuration underpins split DNS. On-premises clients, remote VPN users, and BYOD endpoints must all query the correct DNS server for internal zones while defaulting to public resolvers or split-forwarders for external domains.
-
Windows Server DNS:
- GPO deployment can set internal DNS server addresses en masse for office clients.
- Conditional forwarders direct queries for SaaS or hybrid zones to their external providers.
- AD-integrated DNS dynamically updates for DHCP-issued clients; static entries need pre-staging.
-
BIND:
- Views paired with allow-query/allow-transfer directives enforce split resolution.
- Forwarders handle external domains or cloud service-specific subdomains (e.g., azure.com).
- Zone file reloads are disruptive: changes in critical records need careful coordination to avoid client impact.
-
Netgate pfSense:
- Acts as DHCP server and can push self as DNS resolver to LAN/VPN clients automatically.
- Supports custom forwarders for conditional resolution (e.g., forwarding corp.sg to AD DNS).
- Monitoring tools enable real-time tracking of query success/fail rates; automation via API is limited compared to Windows PowerShell or BIND controls.
Single points of failure—DNS server outages, misconfigured forwarders, or accidental internal zone exposure—are common hazards. The best practice is to pair at least two redundant DNS servers per site, and validate forwarding logic with automated monitoring.
Integrate DNS With Remote Access VPNs
DNS integration is frequently the single most impactful aspect of hybrid team network design. When remote workers connect via VPN, all name resolution requests for internal zones must route only to secure corporate DNS and never “leak” externally. Split-tunnel VPNs require particular attention.
- Full Tunnel VPNs: All traffic, including DNS, flows through the VPN, making configuration simpler. Downsides include higher latency for general browsing and a heavier load on company firewalls.
- Split Tunnel VPNs: Only internal resources pass over the VPN; internet traffic routes directly. DNS suffix search orders and interface metrics must be tuned so internal zones query the VPN DNS, but all other lookups use the client’s default resolver.
Platform nuances:
- Windows Server NPS/RRAS + AD DNS: Group Policy can set NRPT rules for Windows endpoints, ensuring internal namespaces go only to corporate DNS.
- BIND behind OpenVPN/IPsec servers: Tunnel scripts must push DNS options for internal view responses. Inconsistent client support for DNS push (especially on mobile) is a common operational pain point.
- pfSense VPNs: Both OpenVPN and IPsec implementations allow custom DNS server specification in tunnel config. With Active Directory, using RADIUS-based authentication simplifies auto-assignment.
Technical Friction: DNS leaks—when a client’s default resolver answers before the tunnel internal DNS—can undermine split DNS business network security by exposing internal queries to ISPs or hostile networks. Proactive client configuration, regular “leak” testing with public tools, and periodic tunnel script updates are essential to maintain robust segregation.
Align Service Names and Certificates
Split DNS depends not only on correct A/AAAA record resolution but also on consistency between service hostnames and TLS/SSL certificates. Modern browsers, OSes, and API clients are quick to block mismatched certificates even on internal networks. This alignment is critical for services such as Exchange, SharePoint, internal APIs, or VoIP endpoints accessed remotely.
- Certificate Management: For hybrid services reachable via split DNS, use SAN (Subject Alternative Name) certificates listing both public and internal DNS names where feasible.
- Microsoft Environments: Leverage AD CS for internal cert issuance; for externally accessible zones, consider commercial CA with wildcard or UCC certs. Keep in mind, Let’s Encrypt can only verify domains resolvable via public DNS—making true split domains trickier for automation.
- BIND/pfSense Deployments: Internal CA certificate distribution is essential for untrusted devices (BYOD, mobile). Automate certificate renewal and revocation with tools like Certbot (public) or SCEP/ACME servers (internal/private).
Operational Limitation: Changing the FQDN of a legacy service to match a new split DNS scheme may break hard-coded dependencies, SSO flows, or API integrations. Use FQDN aliases judiciously and maintain updated endpoint documentation. Plan phased certificate replacement to avoid outages during critical business periods.
Diagnose Cached and Inconsistent Records
One of the primary operational challenges in running a split DNS business network is cache poisoning or record inconsistency between internal and public views. Common symptoms include:
- Remote employees intermittently unable to reach internal apps after switching networks/VPN states
- DNS query results reflecting outdated IP addresses despite record updates
- SSL certificate errors if cache still points to an obsolete endpoint
Root Causes: Varying TTL values, rogue DHCP/DNS servers on remote LANs, unsynchronized zone file updates, slow AD DS replication (with Windows DNS), or improperly configured BIND views. Cloud-managed devices may also cache answers subject to local resolver limitations.
| Symptom | Potential Root Cause | Troubleshooting Step | Platform-Specific Notes |
|---|---|---|---|
| Stale A/AAAA record on VPN | Long TTLs, outdated zone files | Clear client cache (ipconfig /flushdns, reload network) |
Windows DNS respects AD replication; BIND requires all views reloaded |
| Sporadic NXDOMAIN errors remotely | Split-tunnel DNS leak, local DNS intercept | Verify DNS order, test with nslookup over VPN |
pfSense VPN DNS push may be overruled by client OS priority |
| SSL/TLS mismatch warnings | Clients resolve wrong FQDN view, cert doesn’t match record | Check DNS suffix search order and SAN cert entries | BIND: duplicate zone error likely; Windows: update AD CS cert template |
| Remote access breaks after failover | Secondary DNS not updated, forwarding config incomplete | Check multi-master replication and conditional forwarder settings | Windows: verify DNS Policy status; BIND: ensure all slave servers updated |
To minimize such friction, use automated monitoring solutions that track record propagation (e.g., periodic synthetic queries across internal and cloud test points), enforce low (<12h) TTLs for critical zones, and maintain a rigid change control process for DNS zones and certificates.
Test Access From Office and Remote Networks
Pragmatic validation is essential: end-to-end testing should cover not only resolution but functional access from both office and remote contexts. This confirms that split DNS answers, certificates, and routing all align, and reveals inconsistencies often missed in lab simulations.
-
Testing Checklist:
- Use
nslookupordigto query internal FQDNs from LAN, VPN, and public networks (mobile tether, coffee shop WiFi). - Validate that internal FQDNs are unreachable (NXDOMAIN or private IP) from public resolvers.
- Perform SSL/TLS connection tests (
openssl s_client, web browser connect) to catch CN/SAN mismatches. - Failover DNS servers and simulate VPN drops to check for record propagation and fallback behavior.
- Check application logs for DNS-related errors during handoff between office and remote states.
- Use
Remediation may require adjusting VPN configurations, pushing updated DNS settings to clients, or reissuing certificates. In larger deployments, continuous synthetic testing (DNS probes from cloud and branch offices) is invaluable for early detection of creeping misconfiguration or record divergence.
Assign DNS Ownership and Recovery Procedures
Business resilience requires explicit DNS zone ownership and tested disaster recovery procedures. Split DNS adds two dimensions to continuity planning: both internal and public DNS administrators must coordinate during incidents such as ransomware lockouts, cloud provider outages, or unauthorized DNS changes.
- Ownership Model:
- Appoint primary DNS admins for internal and public views—ideally with cross-training to cover staff absence or turnover.
- Maintain audit trails (Windows DNS logging, BIND logs, pfSense syslog exports) to track record changes and identify unauthorized write attempts.
- Use role-based access for self-service portals if delegating to application owners; restrict public DNS updates to a single approved team.
- Recovery Playbook:
- Backup both internal DNS zone data (AD-integrated zone exports, BIND
zonefiles) and public registrar settings on a weekly basis. - For BIND, maintain at least one offline copy of each view’s zone file; for Windows, use
dnscmdor PowerShell export prior to major changes. - Conduct tabletop exercises where the internal DNS must be rapidly rebuilt from backup or failover to secondary servers during a crisis.
- Publish escalation paths for DNS-related incidents: who owns registrar credentials, how quickly new A/AAAA/CNAME records can be released during emergency re-routes.
- Backup both internal DNS zone data (AD-integrated zone exports, BIND
Legacy practices (single admin, untracked zone edits, lax public DNS registrar security) are unsustainable. Given the criticality of name resolution for every business system, assigning dual backup admins and automating regular offsite backups is non-negotiable. Test both recovery and transfer of DNS ownership rights periodically—particularly in regulated industries or where rapid M&A activity is expected.
Comparative Analysis of Split DNS Technology Stacks
| Platform / Feature | Best For | Internal/External Views | Integration Level | Operating Cost | Automation/API Support | VPN Integration | Limitations |
|---|---|---|---|---|---|---|---|
| Microsoft Windows Server DNS | AD-centric organisations, Windows endpoints | DNS Policy for views, conditional forwarders | Deep AD/LDAP/Group Policy integration | $999+ per Server Standard license | PowerShell, WMI, Dnscmd, 3rd-party tools | Native with RRAS/NPS, GPO deployment | Less agile for BYOD, cross-platform friction, heavy for small sites |
| BIND | Large, OS-diverse networks | Native “views”, zone file granularity | Works with any VPN/firewall, any OS | Free/Open Source, higher admin labor | Key/cert-based updates, Ansible/REST (w/ extension) | Scriptable with any VPN stack | Manual config heavy, error-prone view alignment, no GUI |
| Netgate pfSense (Unbound) | Small/branch offices, rapid deployment needs | Conditional forwarding, internal-only zones | Firewall/DHCP/DNS single appliance | Free (community)/Pro support optional | Basic API, GUI-driven, no robust CLI | Pushes DNS via VPN config, basic DNS leak protection | Limited for multi-site, less granular policy, role-based admin basic |
Summary
A robust split DNS architecture enables Singapore’s hybrid teams—and any geographically dispersed workforce—to use the same intuitive service names in and out of the office, with strong controls over internal service exposure. The setup, while conceptually straightforward, requires relentless attention to integration details, platform idiosyncrasies, SSL/certificate management, and business continuity procedures. Organizations should weigh the breadth of their internal resource map, choose a DNS platform matching their scale and management skills, and include DNS ownership and disaster procedures as core features—not afterthoughts.